
FCSS_NST_SE-7.6 Exam Info and Free Practice Test All-in-One Exam Guide Aug-2026
Pass Fortinet FCSS_NST_SE-7.6 Actual Free Exam Q&As Updated Dump Aug 16, 2026
NEW QUESTION # 25
Refer to the exhibit.
Which three pieces of information does the diagnose sys top command provide? (Choose three.)
- A. The miglogd daemon would be on top of the list, if the administrator pressed m on the keyboard.
- B. If the neweli daemon continues to be in the R state, it will need to be manually restarted.
- C. The diagnose sys top command has been running for 18 minutes.
- D. The cmdbsvr process is occupying 2.4% of the total user memory space.
- E. The miglogd daemon is running on CPU core ID 0.
Answer: A,D,E
NEW QUESTION # 26
Exhibit.
Refer to the exhibit, which shows a FortiGate configuration.
An administrator is troubleshooting a web filter issue on FortiGate. The administrator has configured a web filter profile and applied it to a policy; however the web filter is not inspecting any traffic that is passing through the policy.
What must the administrator do to fix the issue?
- A. Change protocol to TCP.
- B. Enable fortiguard-anycast.
- C. Increase webfilter-timeout.
- D. Disable webfilter-force-off.
Answer: D
Explanation:
The exhibit shows a FortiGate configuration under config system fortiguard related to web filtering and FortiGuard options. There is a line:
set webfilter-force-off enable
According to official Fortinet documentation, the "webfilter-force-off" option, when enabled, causes the FortiGate to bypass web filtering for all traffic-even if a web filter profile is applied to a policy. This override is typically used for troubleshooting or performance reasons and is documented as an explicit bypass feature.
If an administrator wants to enforce web filtering inspection, this setting must be disabled. The correct way to restore web filtering functionality is to run:
set webfilter-force-off disable
Once done, traffic passing through policies with web filter profiles will be inspected and filtered as per configuration. Other settings such as timeout or cache TTL do not bypass web filtering; they only affect operational nuances.
Reference:
FortiOS Administration Guide: Web Filtering, FortiGuard Options, "webfilter-force-off" CLI
NEW QUESTION # 27
Which authentication option can you not configure under config user radius on FortiOS?
- A. mschap2
- B. pap
- C. eap
- D. mschap
Answer: C
NEW QUESTION # 28
Refer to the exhibit, which shows the partial output of a diagnose command.
Which two conclusions can you draw from the output shown in the exhibit? (Choose two.)
- A. FortiGate will drop the expected traffic if it does not arrive within 23 seconds.
- B. Clearing the master session has no impact on the expectation session.
- C. This is a pinhole session to allow traffic for a TCP protocol that dynamically assigns TCP ports.
- D. The session is checked against firewall policy ID 25.
Answer: A,C
NEW QUESTION # 29
Refer to the exhibit, which a network topology and a partial routing table.
FortiGate has already been configured with a firewall policy that allows all ICMP traffic to flow from port1 to port3.
Which changes must the administrator perform to ensure the server at 10.4.0.1/24 receives the echo reply from the laptop at 10.1.0.1/24?
- A. Enable asymmetric routing under config system settings.
- B. Modify the default gateway on the laptop from 10.1.0.2 to 10.2.0.2.
- C. A firewall policy that allows all ICMP traffic from port3 to port1.
- D. Change the configuration from strict RPF check mode to feasible RPF check mode.
Answer: A
NEW QUESTION # 30 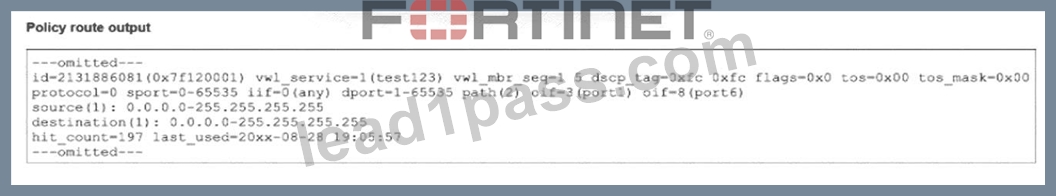
The output of a policy route table entry is shown.
Which type of policy route does the output show?
- A. A regular policy route, which is not associated with an active static route in the FIB
- B. A regular policy route, which is associated with an active static route in the FIB
- C. An ISDB route
- D. An SD-WAN rule
Answer: D
Explanation:
To determine the type of policy route, we must interpret the specific flags and fields visible in the diagnose firewall proute list (or similar kernel table) output provided in the exhibit Identify Key Indicators:
The most critical field in the output is vwl_service=1(test123).
It also lists vwl_mbr_seq=1 5.
Decode the Terminology:
vwl: This stands for Virtual WAN Link. In FortiOS, " Virtual WAN Link " is the legacy internal name for the SD-WAN feature. Even in newer firmware versions (7.x), the kernel and CLI debugs often still refer to SD- WAN objects as vwl.
vwl_service: This specifically refers to an SD-WAN Rule (also known as an SD-WAN Service). The name (test123) is the name given to that specific SD-WAN rule by the administrator.
Evaluate the Options:
A & D (Regular Policy Route): Standard policy routes (configured under config router policy) do not carry the vwl_service tag. They are typically identified by simple gateway or interface instructions without the SD- WAN service abstraction.
B (ISDB Route): While SD-WAN rules can use the Internet Service Database (ISDB) as a destination, the structure of the route entry shown here-specifically defined by a vwl_service ID-classifies it fundamentally as an SD-WAN rule, regardless of the destination object.
C (An SD-WAN rule): The presence of vwl_service and vwl_mbr_seq (SD-WAN member sequence) definitively identifies this entry as a rule generated by the SD-WAN subsystem.
Conclusion: The output shows a route controlled by the SD-WAN engine (vwl), confirming it is an SD-WAN rule.
Reference:
FortiGate Security 7.6 Study Guide (SD-WAN): " In the kernel routing table and debugs, SD-WAN rules are often referenced as vwl (Virtual WAN Link) services. The vwl_service field indicates the specific SD-WAN rule ID and name. "
NEW QUESTION # 31
Refer to the exhibit, which shows the output of a diagnose command. What can you conclude from the RTT value?
- A. Its value is incremented with each packet lost.
- B. Its value represents the time it takes to receive a response after a rating request is sent to a particular server.
- C. Its initial value is statically set to 10.
- D. It determines which FortiGuard server is used for license validation.
Answer: B
Explanation:
The correct answer is A.
The study guide explicitly explains the diagnose debug rating table and says that for each server IP, the output shows "The round trip delay" That means the RTT value represents the time it takes for FortiGate to send a request and receive the reply from that FortiGuard server.
The FortiOS administration guide also confirms this by stating:
"Each server is probed for Round Trip Time (RTT) every two minutes."
Why the other options are wrong:
B is wrong because packet loss is shown separately by Curr Lost and Total Lost, while RTT is the round-trip delay C is wrong because license-validation behavior is indicated by flags such as I = Initial, not by the RTT value itself D is wrong because the documents do not say RTT starts at a fixed value of 10; it is measured dynamically as round-trip delay So the verified answer is: A.
NEW QUESTION # 32
Refer to the exhibits.
An administrator is attempting to advertise the network configured on port3. However, FGT-A is not receiving the prefix.
Which two actions can the administrator take to fix this problem? (Choose two.)
- A. Modify the prefix using the network command from 172.16.0.0/16 to 172.16.54.0/24.
- B. Manually add the BGP route on FGT-A.
- C. Restart BGP using a soft reset to force both peers to exchange their complete BGP routing tables.
- D. Use the set network-import-check disable command.
Answer: A,D
NEW QUESTION # 33
Refer to the exhibit, which shows the output o! the BGP database.
Which two statements are correct? (Choose two.)
- A. The output shows all prefixes advertised by all neighbors as well as the local router.
- B. The advertised prefix of 10.20.30.0/24 was configured using the network command.
- C. The advertised prefix of 10.20.30.0/24 is being advertised through the redistribution of another routing protocol.
- D. The first four prefixes are being advertised using a legacy route advertisement.
Answer: A,B
Explanation:
For Option A:In Fortinet BGP (and standard BGP), when a prefix is displayed with an " i " (lowercase i) in the Path column, it represents an internal prefix that originated from the local router, typically configured via the BGP " network " command. In the exhibit, the prefix 10.20.30.0/24 is listed with a Path value of i, indicating it was injected into BGP by the local router using the network statement, not via redistribution from another routing protocol. The same logic applies to i as documented: " Origin code ' i ' means the route was injected via the network command. " For Option D:The get router info bgp network output is a summary table displaying both local and received BGP routes. It lists all known routes to the BGP process, whether received from peers or originated locally.
The exhibit shows all BGP prefixes known to the local router, matching the official admin guide's description of this command's output.
Explanation for B and C:
The phrase "legacy route advertisement" is not formalized in BGP documentation or Fortinet's admin guide; the output uses standard BGP mechanics.
If a route was redistributed into BGP from another routing protocol, the Path field would display a " ? " (question mark) for incomplete (redistributed) origin. Here the /24 route has " i " so it is NOT a redistribution.
References:
FortiOS Administration Guide: BGP Configuration and Route Table Interpretation Official BGP Command Reference: Show BGP Network, Path Codes, Route Origination Indicators
NEW QUESTION # 34
Refer to the exhibit.
A partial output from an IKE real-time debug is shown
The administrator does not have access to (he remote gateway
Based on the debug output, which two conclusions can you draw? (Choose two.)
- A. This is a phase1 negotiation.
- B. There is a Diffie-Hellman group mismatch.
- C. This is a phase2 negotiation
- D. The remote peer is the initiating peer.
Answer: A,D
Explanation:
To determine the correct conclusions, we analyze the specific lines in the IKE real-time debug output provided in the exhibit:
Analysis for Option A (The remote peer is the initiating peer):
Evidence: The very first line of the debug output reads: ike 0:624000:98: responder: main mode get 1st message...
The keyword responder indicates that this local FortiGate is receiving the connection request. Consequently, the remote peer must be the initiator sending the request. The phrase "get 1st message" confirms the local unit is receiving the initial packet of the negotiation sequence.
Conclusion: This statement is True.
Analysis for Option B (This is a phase 1 negotiation):
Evidence: The same line mentions main mode.
In IPsec VPNs, Main Mode and Aggressive Mode are exclusively used for Phase 1 (IKE SA) negotiations.
Phase 2 (Child SA) negotiations use Quick Mode. The presence of "main mode" definitively identifies this as a Phase 1 exchange.
Conclusion: This statement is True.
Analysis for Option C (There is a Diffie-Hellman group mismatch):
Evidence:
Incoming proposal (Remote): Lists type=OAKLEY_GROUP, val=MODP2048 (Group 14) in the first proposal proposal.
My proposal (Local): Lists type=OAKLEY_GROUP, val=MODP2048 (Group 14).
Since both the remote peer and the local gateway support and are proposing MODP2048 (Group 14), there is no Diffie-Hellman group mismatch. The actual mismatch visible in the logs is between the Encryption/Hash algorithms (Remote proposes AES-256/SHA2-256, while Local proposes AES-128/SHA), but the DH groups match.
Conclusion: This statement is False.
Analysis for Option D (This is a phase 2 negotiation):
As established in the analysis for Option B, "Main Mode" is a Phase 1 protocol. If this were Phase 2, the debug would show "Quick Mode".
Conclusion: This statement is False.
Reference:
FortiGate Security 7.6 Study Guide (IPsec VPN): "Phase 1 modes: Main mode and Aggressive mode." FortiOS Debugging documentation: Explains that "responder" indicates the device receiving the IKE initialization.
NEW QUESTION # 35
Refer to the exhibit.
The output of diagnose sys session list command is shown.
If the HA ID for the primary device is 9, what happens if the primary fails and the secondary becomes the primary?
- A. The session will be removed from the session table of the secondary device because the TCP session is not yet fully established.
- B. The session is synchronized with the secondary device, however, because application control is applied.
the session is marked dirty and has to be reevaluated after failover. - C. The session continues to permit traffic on the new primary device after failover. without requiring the client to restart the session with the server.
- D. The session state is preserved but the kernel will re-evaluate the session because the routing information will be flushed
Answer: C
Explanation:
The output of the diagnose sys session list command provides the critical evidence needed to determine the behavior during a failover:
* Session Synchronization (synced):
* The most important indicator in the exhibit is the synced flag located in the state= line (state=may_dirty synced none app_ntf).
* In FortiOS HA (High Availability), the synced flag confirms that this specific session has been successfully synchronized from the primary device to the secondary (backup) device.
* Session synchronization (Session Pickup) ensures that if the primary unit fails, the secondary unit already has the session in its table and can resume traffic processing immediately.
* TCP State (proto_state=01):
* The output shows proto=6 (TCP) and proto_state=01.
* In the FortiGate session table, proto_state=01 for TCP indicates that the session is in the ESTABLISHED state (post-three-way handshake).
* This invalidates Option B, which claims the TCP session is not fully established.
* Failover Outcome:
* Because the session is ESTABLISHED and SYNCED, the secondary device will seamlessly take over the session upon primary failure.
* The traffic continues to flow through the new primary without requiring the user/client to restart the connection. This is the primary function of HA Session Pickup.
Why other options are incorrect:
* A: While the output shows app_ntf (Application Control notification) and may_dirty, the presence of the synced flag overrides this concern regarding failover. If the session type were not supported for failover (e.g., certain proxy sessions in older versions), it would not be marked as synced. Since it is synced, it persists.
* B: As noted, proto_state=01 means established, not "not fully established".
* D: While the kernel updates routing tables, the purpose of syncing the session is to preserve the state so it does not need to be re-evaluated as a new packet would, preventing traffic drops.
Reference:
FortiGate Security 7.6 Study Guide (High Availability): "If session pickup is enabled, the primary unit synchronizes its session table... to the backup unit. If the primary unit fails, the backup unit... continues to process the sessions with no interruption."
NEW QUESTION # 36
Which statement about IKEv2 is true?
- A. IKEv1 and IKEv2 use same TCP port but run on different UDP ports.
- B. Both IKEv1 and IKEv2 share the feature of asymmetric authentication.
- C. IKEv1 and IKEv2 have enough of the header format in common that both versions can run over the same UDP port.
- D. IKEv1 and IKEv2 share the concept of phase1 and phase2.
Answer: C
NEW QUESTION # 37
Refer to the exhibit, which shows the partial output of FortiOS kernel slabs.
Which statement is true?
- A. The total slab size of the ip6_session slab is 1300 kB and is associated with the kernel.
- B. The total slab size of the tcp_session slab is 7500 kB and is associated with the kernel.
- C. The total slab size of the ip_session slab is 3600 kB and is associated with the user space.
- D. The total slab size of the sctp_session slab is 0 kB and is associated with the user space.
Answer: B
NEW QUESTION # 38
Exhibit.
Refer to the exhibit, which shows the output of a diagnose command.
What can you conclude about the debug output in this scenario?
- A. There is a natural correlation between the value in the FortiGuard-requests field and the value in the Weight field.
- B. Servers with a negative TZ value are less preferred for rating requests.
- C. The first server provided to FortiGate when it performed a DNS query looking for a list of rating servers, was 121.111.236.179.
- D. FortiGate used 64.26.151.37 as the initial server to validate its contract.
Answer: D
Explanation:
The exhibit displays the output from the diagnose debug rating command on a FortiGate device. This command is used to display information about FortiGuard Web Filtering or other security-related queries performed by FortiGate to FortiGuard servers. Official Fortinet documentation outlines the meaning of each field in the server list. The FortiGate maintains a list of available FortiGuard servers, selecting the optimal server based on factors such as weight, round-trip time (RTT), and regional settings.
The very first entry in the server list after "Server List" is the server FortiGate initially uses, prioritized by factors such as proximity and RTT. Here, 64.26.151.37 is listed first, and the FortiGuard-requests value confirms that this server handled the highest number of requests.
The IPs, weights, and lost/failed counters are monitored for server performance and selection over time. FortiGate's default operational logic is to try the first entry for contract validation and use the next in the list if the first is unavailable or has high latency or packet loss.
There is no direct correlation between the Weight and the number of FortiGuard-requests. The servers with higher or lower weights may still handle different request volumes based on availability and performance.
The TZ (time zone) value's sign (positive or negative) does not affect server preference; it is informational, showing the server's location relative to UTC, not a rating metric.
DNS query results for FortiGuard servers are not shown here, and the provided servers are not returned in DNS query order.
This command and interpretation are detailed in the FortiOS Administration Guide's section describing FortiGuard server selection and contract validation processes.
References:
FortiOS Administration Guide: FortiGuard Service Connectivity and Debugging Official Technical Notes on diagnose debug rating output structure
NEW QUESTION # 39
What can cause an IKEv2 tunnel to go down after it was initially brought up successfully?
- A. A mismatched pre-shared key was detected during the IKE_AUTH exchange.
- B. A mismatched proposal was detected during the IKE_AUTH exchange.
- C. A mismatched Diffie-Hellman group was detected during the IKE_SA_INIT exchange.
- D. Mismatched quick-mode selectors were detected during the CREATE_CHILD_SA exchange.
Answer: D
Explanation:
The correct answer is D.
The study guide explains that IKEv2 has two initial exchanges:
IKE_SA_INIT
IKE_AUTH
and then later exchanges such as:
CREATE_CHILD_SA
It also states the roles of those exchanges:
IKE_SA_INIT negotiates the security settings for IKE traffic
IKE_AUTH performs mutual authentication and sets up the piggyback child SA CREATE_CHILD_SA creates a new child SA or rekeys an existing child SA Most importantly, the study guide explicitly says:
"By IKEv2 design, no Diffie-Hellman public key is exchanged during an IKE_AUTH exchange. Consequently, any phase 2 Diffie-Hellman group configuration mismatch between FortiGate and the peer is experienced only during the first rekey (CREATE_CHILD_SA exchange) of the child SA created during IKE_AUTH." This proves the key idea behind the question: an IKEv2 tunnel can come up successfully first, then fail later during a CREATE_CHILD_SA rekey/renegotiation event because of a phase 2 mismatch. Among the provided options, the matching later-stage cause is mismatched quick-mode selectors during CREATE_CHILD_SA.
Why the other options are wrong:
A is wrong because if the proposal mismatch were in the initial negotiation path, the tunnel would fail during establishment, not after it was already up. The study guide places initial tunnel establishment in IKE_SA_INIT and IKE_AUTH B is wrong because a mismatch in IKE_SA_INIT affects the initial establishment stage, not a tunnel that was already brought up successfully C is wrong because a pre-shared key mismatch is part of authentication during IKE_AUTH, so the tunnel would not come up successfully in the first place
NEW QUESTION # 40
Exhibit 1.
Exhibit 2.
Refer to the exhibits, which show the configuration on FortiGate and partial internet session information from a user on the internal network.
An administrator would like to lest session failover between the two service provider connections.
Which two changes must the administrator make to force this existing session to immediately start using the other interface? (Choose two.)
- A. Configure set snat-route-change enable.
- B. Change the priority of the port1 static route to 11.
- C. Change the priority of the port2 static route to 5.
- D. Configure unset snat-route-change to return it to the default setting.
Answer: A,B
Explanation:
FortiOS Admin Guide: Static Routing, SNAT Route Change Feature
NEW QUESTION # 41
......
Fortinet FCSS_NST_SE-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
Online Questions - Valid Practice FCSS_NST_SE-7.6 Exam Dumps Test Questions: https://simplilearn.lead1pass.com/Fortinet/FCSS_NST_SE-7.6-practice-exam-dumps.html